1. Beyond Fragile Virtual Machines
Traditional enterprise infrastructure often relied on long-lived virtual machines (EC2 instances) configured manually or through disparate scripts. Over time, configuration drift, manual patch updates, and unpredictable scaling latencies make such environments fragile and expensive to maintain.
Modern enterprise cloud engineering mandates immutable containerized infrastructure. By packaging applications into self-contained Docker images and orchestrating them via serverless container runtimes, engineering teams achieve sub-minute scaling, predictable environment parity, and automated zero-downtime deployments.
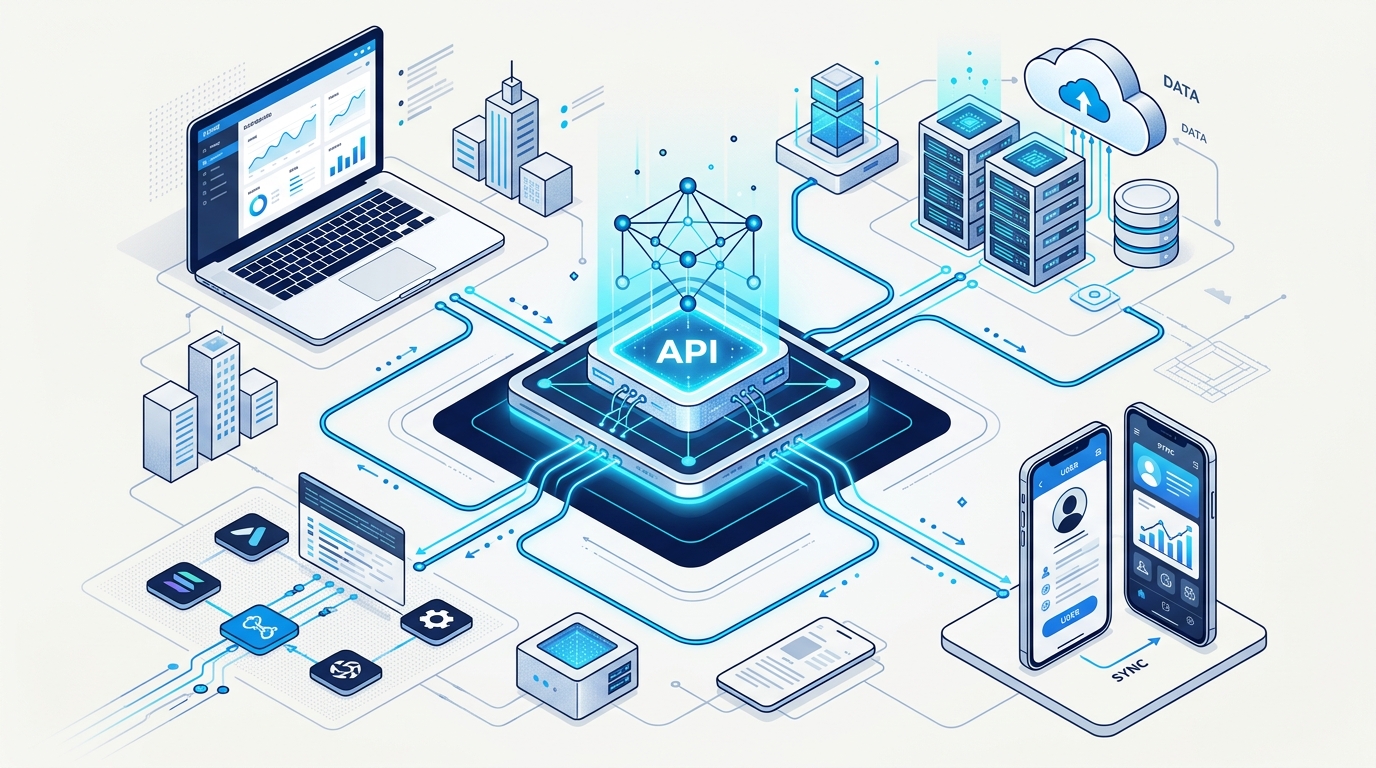
2. Core AWS Production Architecture Topology
At ByteStream, we architect enterprise container deployments on AWS following a multi-tier, defense-in-depth network topology:
1. Public Ingress Tier
- AWS WAF (Web Application Firewall): Inspects incoming HTTP/S traffic, blocking SQLi, XSS, and rate-limiting IP floods.
- Amazon CloudFront & Route 53: Low-latency global CDN for static asset caching and intelligent DNS failover.
- Application Load Balancer (ALB): Terminates TLS certificates (AWS Certificate Manager), executes health checks, and routes requests to container target groups.
2. Private Compute Tier (ECS / Fargate)
- Amazon ECS with AWS Fargate: Serverless container execution eliminating the overhead of managing underlying EC2 operating systems or cluster patching.
- Multi-AZ Distribution: Container tasks are automatically balanced across at least 2 Availability Zones for high availability.
- Target Tracking Auto-Scaling: Automatically adds or removes container tasks based on CPU, memory, or request count per target.
3. Isolated Data Tier
- Amazon RDS (PostgreSQL / MySQL): Multi-AZ deployment with automated failover, read replicas for high-throughput queries, and encrypted EBS volumes.
- Amazon ElastiCache (Redis): Microsecond-latency distributed session cache, rate-limiting store, and pub/sub message broker.
- Amazon S3: Encrypted object storage for user documents, media files, and automated backups.
3. Automated Zero-Downtime CI/CD Pipeline
A resilient cloud architecture is incomplete without an automated, reproducible deployment pipeline. Our standard GitHub Actions / AWS CodePipeline workflow enforces quality gates before code reaches production:
Stage 1: Commit & Quality Gates
On pull request merge to main, automated runners execute code formatting checks, static analysis (SAST), and unit test suites.
Stage 2: Immutable Docker Image Build & Scan
The application is built into a minimal Docker container (using Alpine or distroless base images). The container image is scanned for CVE vulnerabilities (via Trivy / Amazon ECR image scanning) and tagged with the git commit SHA.
Stage 3: Rolling Zero-Downtime Deployment
ECS initiates a rolling deployment: new container tasks are launched, pass target group health checks, and begin receiving traffic before old container tasks are gracefully drained and stopped. Users experience zero interruption or downtime during deployments.
4. Security Isolation & Cost Optimization Strategies
- IAM Roles for Tasks: Container applications receive fine-grained IAM permissions at the individual task level rather than inheriting broad EC2 instance permissions.
- Zero Ingress Database Security Groups: Database security groups accept ingress traffic strictly from container security groups on port 5432/3306—completely isolated from the public internet.
- Fargate Spot for Background Workers: Run asynchronous queue workers, scheduled cron tasks, and batch jobs on Fargate Spot at up to a 70% cost reduction compared to standard on-demand pricing.
- Automated CloudWatch Alarms: Proactive telemetry monitoring 5xx error rates, database connection pool saturation, and memory thresholds with instant engineer Slack/email alerts.